
The opportunity for bank presidents and boards of directors is not to automate professional judgment, but to equip professionals with better tools to act.
By Mijares Consulting
Key Takeaways
AI is already transforming Compliance: The debate has shifted from whether banks will use it to how they can implement it safely, effectively, and with appropriate governance.
The goal is not to generate more alerts, but to make better decisions: AI can help reduce noise, prioritize investigations, and direct compliance resources toward the most relevant cases.
From KYC and KYT to “Know Your Context”: Beyond knowing the customer and their transactions, AI makes it possible to incorporate context, expected behavior, comparable peer groups, and historical changes to better understand risk.
Models should be specialized: XGBoost can support alert prioritization, temporal models such as LSTM can analyze transaction patterns, and large language models (LLMs) can help interpret and explain results.
AI should support, not replace, compliance professionals: Material decisions must remain under human control. Our approach uses explainable AI and keeps the investigator as the final decision-making authority.
Explainability is essential: Probabilities, priority levels, model confidence, and SHAP factors help explain why a case received a particular classification, rather than relying on a “black box.”
The objective of a compliance program should not be to produce more alerts. It should be to better identify what deserves investigation, act promptly, and substantiate every decision.
With that premise, we recently participated in a compliance conference in Puerto Rico, where we presented the session “AI in Compliance: Transforming Monitoring and Decision-Making. Less Noise, Better Alerts, and Higher-Quality Decisions with AI.”
In addition to discussing technology, we demonstrated our artificial intelligence application designed to support transactional activity analysis and alert prioritization.
Our main takeaway from the conference is this: the value of AI in Compliance is not simply its ability to process more data. It is its ability to help banks better understand what is happening, what deserves attention, and what evidence is needed before making a decision.
From Knowing the Customer to Understanding Their Context
One of the most interesting ideas discussed during the conference was expanding the focus from Know Your Customer (KYC) and Know Your Transaction (KYT) to Know Your Context.
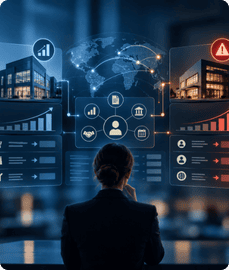
Knowing who a customer is and how much money they move does not always sufficiently explain their behavior. It is also important to understand their economic activity, business relationships, seasonality, counterparties, and how their activity evolves compared with what could reasonably be expected.
Consider two companies that double their international transfers. One may be responding to a documented seasonal increase in sales. The other may be sending funds to new counterparties without a verifiable business justification. The numerical increase is similar, but the questions an investigator should ask are different.
This is the type of analysis we seek to strengthen through AI: connecting information that, when examined separately, may be insufficient.
There is also a commercial implication. A more contextualized assessment can help prevent indiscriminate de-risking: restricting or terminating relationships with entire categories of customers without adequately evaluating their individual circumstances.
Regulators have advocated for case-by-case assessments and have recognized that new technologies, when used responsibly, can improve both compliance effectiveness and financial inclusion.
Better understanding risk does not mean accepting every relationship. It means having stronger grounds to maintain a relationship, impose additional controls, or terminate it.
What We Demonstrated: Specialized Models, Not One AI That Does Everything
Our approach begins with an important distinction: prioritizing alerts, identifying changes in behavior, and drafting an analysis are different tasks. They should not be treated as the same problem.
The architecture presented combines three functions:
XGBoost for Alert Prioritization: XGBoost uses structured customer and activity information to assign scores and prioritize cases for review. The application includes explanations of the factors influencing the results, so investigators receive more than a number. They receive information they can question and evaluate.
LSTM for Temporal Analysis: LSTM is a component designed for temporal analysis. This type of neural network works with sequences, allowing it to examine not only an isolated activity but also how that activity evolves over time. In the documented prototype, LSTM remains experimental. Its use in temporal monitoring requires training and evaluation with appropriate chronological transaction histories.
Large Language Models (LLMs) to Support Analysis and Communication: LLMs help analyze and communicate findings. Their role is to transform model results and available context into explanations that investigators and management can understand. They do not replace evidence or make final decisions.
The demonstration uses synthetic data to illustrate this approach. It should not be confused with effectiveness results already proven within a bank.
Moving into production requires evaluating the models using representative data and, for alert prioritization, actual investigation outcomes.
The operating principle is straightforward: AI organizes information and provides signals; the professional investigates, reviews, and approves.
The application does not automatically close alerts, establish suspicious activity as fact, or decide whether a Suspicious Activity Report (SAR) should be filed.
Professional Judgment Does Not Disappear. It Must Be Better Supported.
Another important warning raised during the conference was that language models may fill gaps left by our instructions.
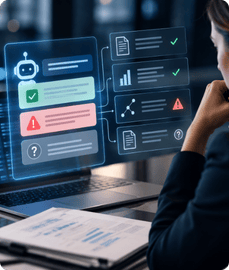
It is important to clarify the risk: ambiguous instructions or incomplete information can contribute to incorrect responses, but even well-written instructions do not eliminate hallucinations. NIST describes this problem as the generation of false or erroneous content presented with apparent confidence. A convincing explanation is not necessarily a correct explanation.
For this reason, our approach requires distinguishing verified facts from inferences, presenting the available evidence, and identifying missing information. When sufficient supporting evidence does not exist, the appropriate response may be “requires further review,” rather than a more elaborate conclusion. Human oversight must also be more than an automatic sign-off.
Reviewers need sufficient time, expertise, and authority to disagree with the system. NIST warns about automation bias: placing excessive trust in a response simply because it was generated by an automated system.
We also recommend controlled learning. Investigation outcomes may inform future model retraining, but changes must be tested, documented, and approved.
“The model learns” should never mean “the model changes without oversight.”
AI Is Already Here. Its Value Must Be Demonstrated.
The public conversation has moved from asking whether AI will have an impact to debating how that impact should be directed.
On September 22, 2026, during his address to the United Nations General Assembly, President Donald Trump used the expression “Super Intelligence” to refer to artificial intelligence.
For a board of directors, that terminology should not be confused with demonstrated technical capability or reliability.
Source: whitehouse.gov
The most useful evidence for a bank comes from testing.
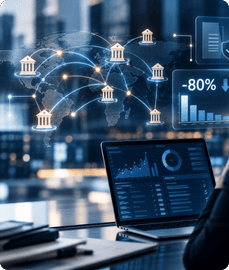
For example, the first phase of the Bank for International Settlements’ Project Aurora explored AI, network analytics, and collaboration among institutions in simulated scenarios. It reported reductions in false positives of up to 80%. This was a result from a specific proof of concept, not a guarantee that can be transferred to any bank, nor a result achieved by our application. Its relevance lies in demonstrating potential that must be verified in each environment. Source: Bank for International Settlements
Regulatory discussions are also increasingly focused on effectiveness. In its April 2026 proposal to reform AML/CFT programs, FinCEN proposed directing more resources toward higher-risk customers and activities. That proposal must be distinguished from a final rule and, certainly, from any requirement to use AI. Source: FinCEN.gov
Our interpretation is practical: discussions with management should not be limited to how much technology has been purchased, but should focus on which decisions have improved and what evidence demonstrates that improvement.
What a Board of Directors Should Measure
An important distinction must be made: better alert prioritization does not, by itself, mean fewer false positives. Changing the order of a queue does not eliminate the items within it. Improvement must be evaluated against the existing process.
For a pilot, we recommend answering three questions:
Are We Improving Investigations?
Evaluate whether relevant cases reach investigators sooner, whether explanations are useful, and whether important cases are being assigned low priority.
Are We Improving Operations?
Measure review times, backlogs, rework, and cost per case, including integration, oversight, and maintenance.
Are We Maintaining Control?
Verify data protection, human review, exception documentation, and the ability to stop or modify the system if its performance deteriorates.
We do not recommend measuring success solely through an overall accuracy rate or the number of alerts closed. For the board, the relevant question is whether the bank is making better use of its resources without weakening risk identification and management.
A Straightforward Approach to AI Adoption for Banks
A bank president does not need to become a data scientist to lead responsible AI adoption. What is needed is a clearly defined problem, verifiable results, and clear accountability.
At Mijares Consulting, we recommend starting with the operational challenge: too many pending alerts, fragmented information, repetitive investigations, or difficulty explaining results to management.
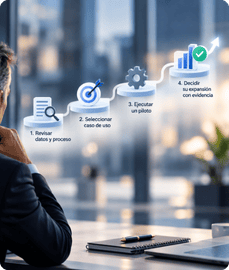
From there, we structure a manageable path: review the data and the process, select a use case, execute a narrowly scoped pilot, and determine whether to expand based on evidence.
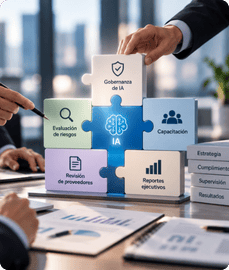
Where appropriate, we recommend initially running the pilot alongside the existing process, without delegating sensitive decisions. Our support combines solution design with AI governance, risk assessment, vendor review, training, and executive reporting, while preserving the independence required for validation. Management receives a defined scope, understandable deliverables, and clear decision points for approving and adjusting the project.
Convenience does not mean eliminating controls. It means the bank does not have to coordinate every component of the solution on its own.
The reflection we brought back from Puerto Rico is that AI becomes far more useful when it stops being presented as a technological promise and becomes a response to a concrete compliance problem.
That is the starting point we propose: identify where time is being lost, where context is missing, and which decision needs improvement; then demonstrate how to solve it while keeping the bank in control.
Follow us, stay informed, stay secure, and let’s navigate the risk landscape together.